Security
Reporting a vulnerability. Email [email protected]. Include a description, affected version, and reproduction steps. We acknowledge within two business days, keep you informed, and credit you in the advisory if you wish. Please give us 90 days before public disclosure.
Scope. The Janus Edge gateway (all editions), this website and the customer portal. Out of scope: third-party providers you connect the gateway to, and social engineering.
How Janus Edge is built to be safe by default
- Prompts and responses are never stored unless an administrator opens an explicit, time-boxed troubleshooting session with a filter and retention limit.
- Encryption at rest for provider credentials and captured data with a key you control.
- Authentication by OIDC Authorization Code + PKCE; dev sign-in refuses to start on non-loopback URLs in production.
- Every administrative action is written to an append-only audit log.
- Release images are built from the published source tag, signed with cosign, scanned with Trivy, and ship with an SBOM.
- Offline license verification: no outbound calls are required to run.
Questionnaires. Business and Enterprise customers can request a completed CAIQ-Lite / SIG-Lite, our data-handling summary and the latest self-assessment report from the portal.
Advisories. Published in the changelog and the GitHub Security Advisories for the public repository. Security releases are flagged in the gateway's update notice.
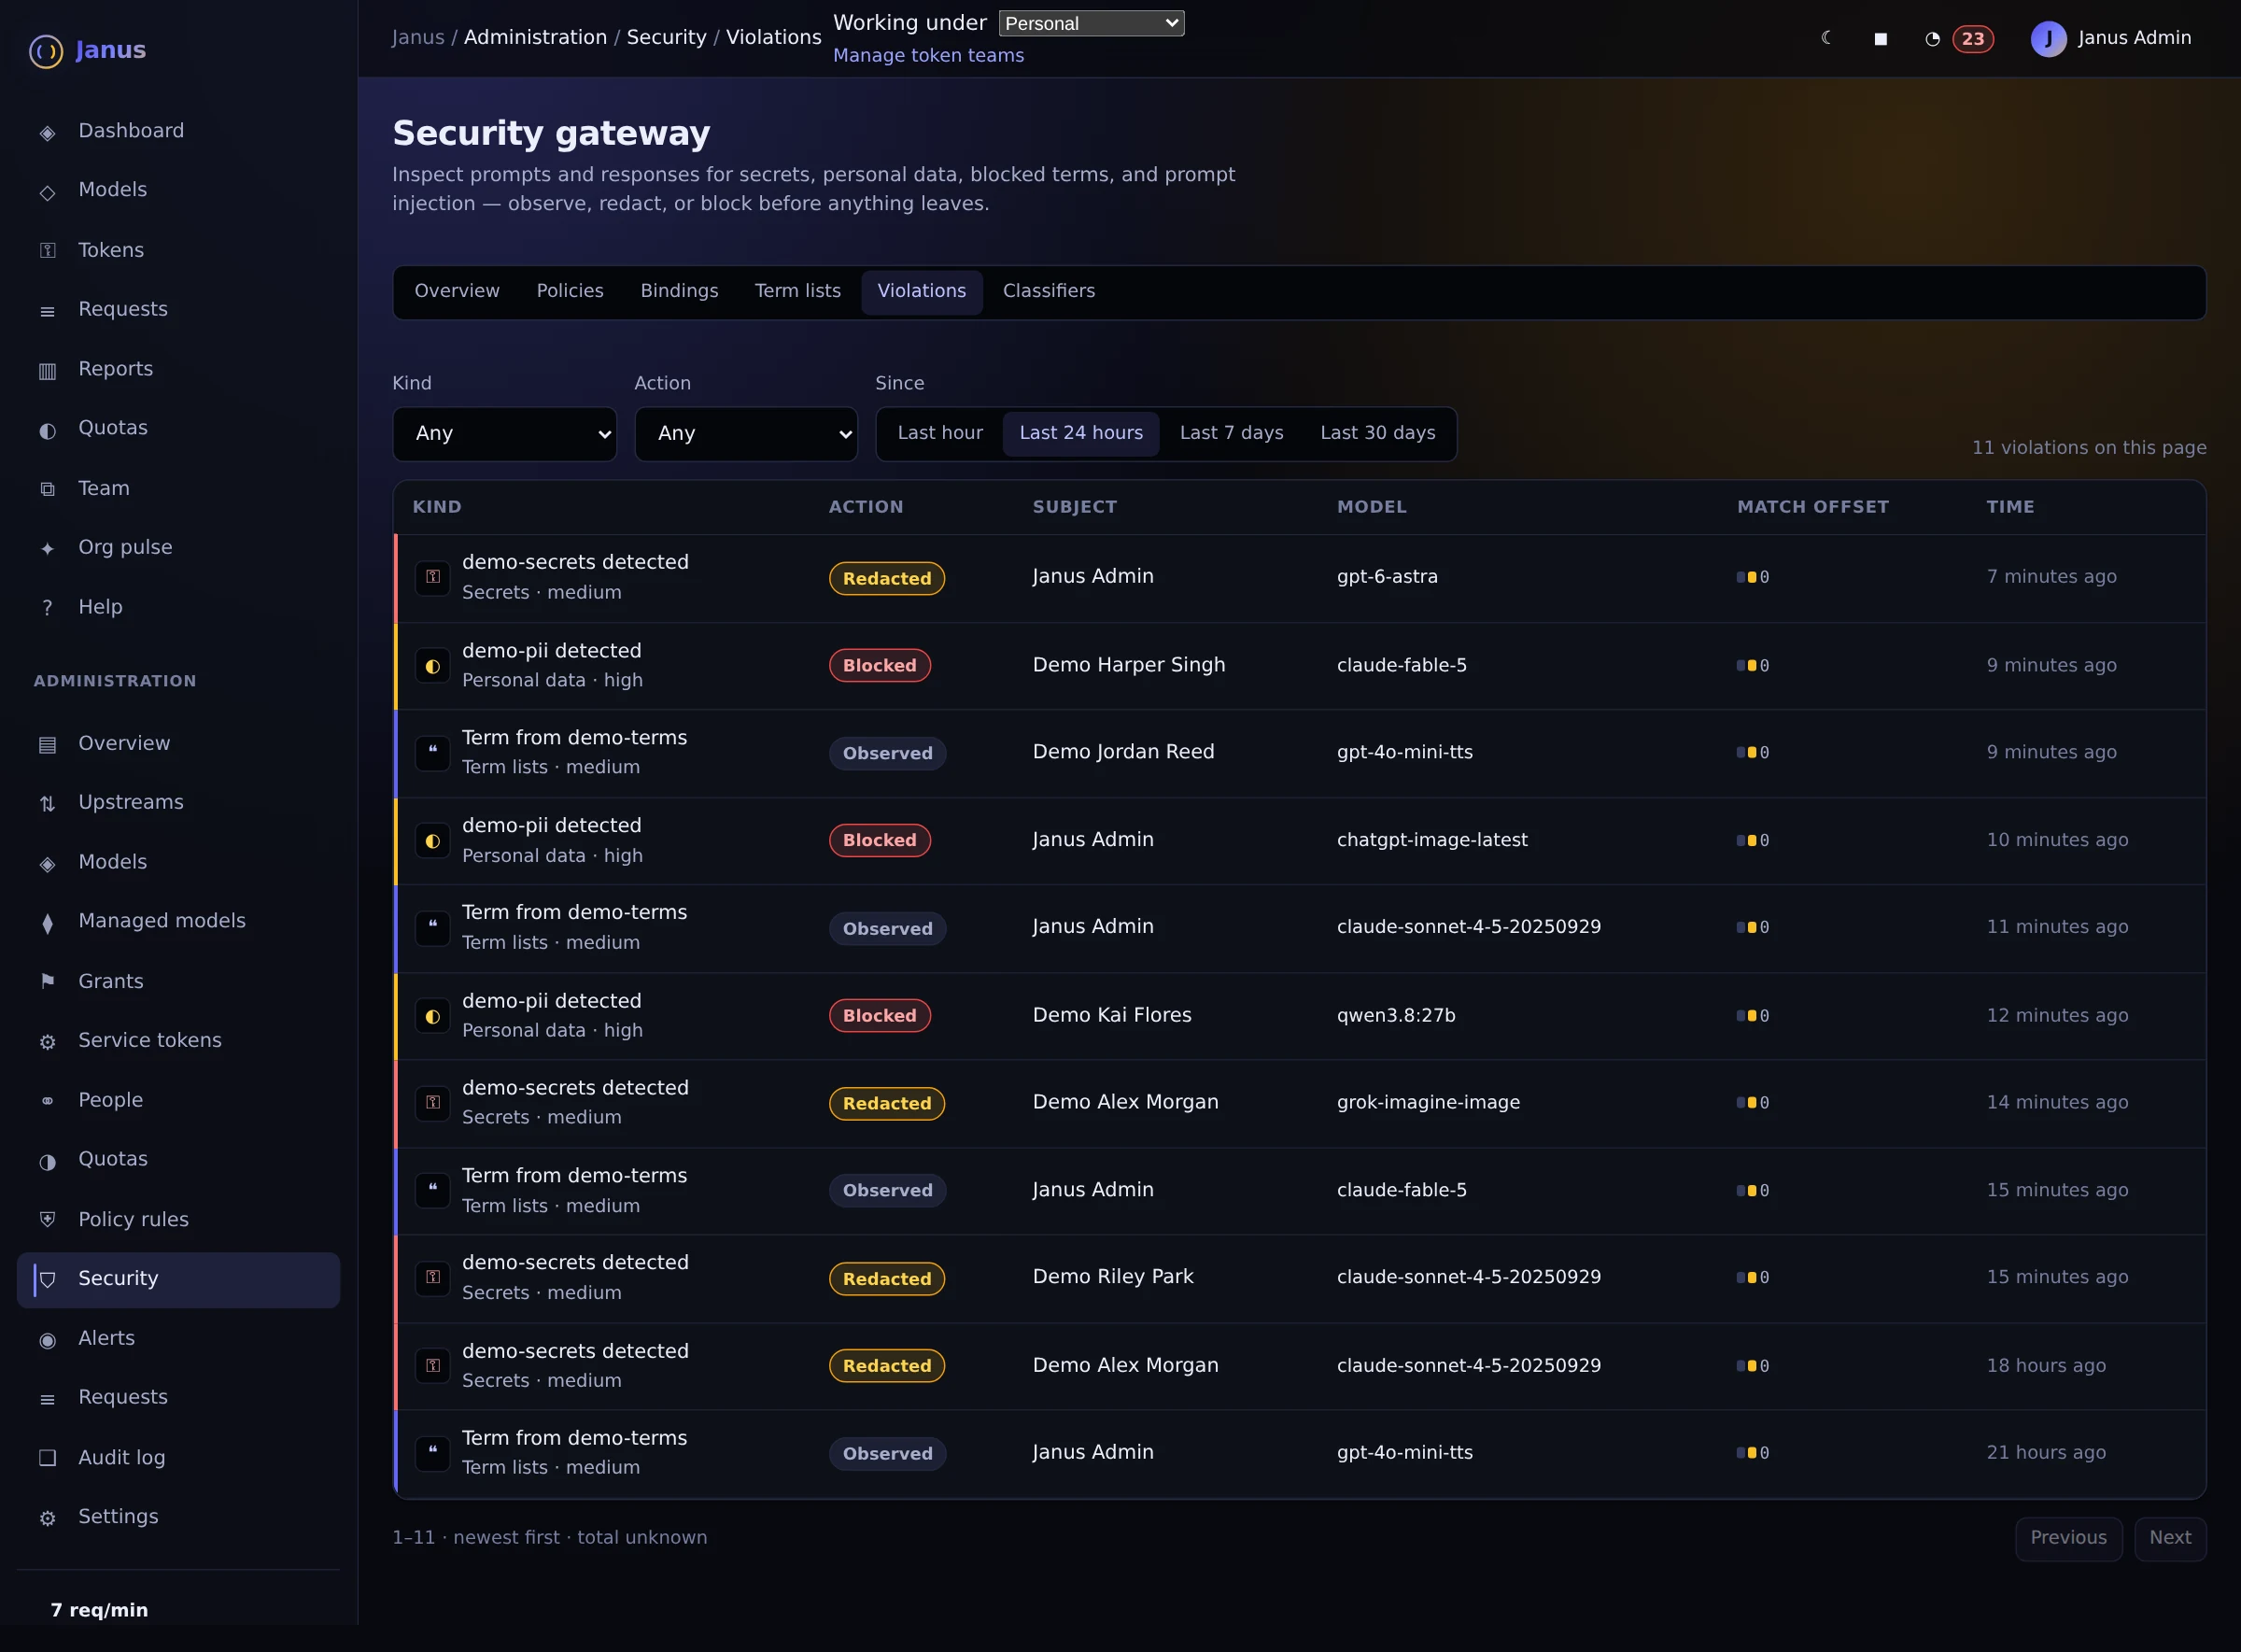
Filter historical findings by policy, detector, severity, and action. Investigate without exposing prompt contents.
Actual Janus interface · Demo identities and synthetic usage